Requests that survive retries
A Python API validates requests, checks ownership and uses atomic DynamoDB writes. Repeating the same request with the same key returns the existing record instead of creating a duplicate.
Built by Anrotex
Cloud Operations brings an authenticated requests API, repeatable AWS infrastructure and a tested release procedure together in one engineering project.
A retry should not create a duplicate operation. A deployment should prove that the application works. And a failed release should leave the team with a clear recovery action. We built Cloud Operations to connect those decisions in a small, inspectable system.
The API records operational requests; it does not execute infrastructure changes submitted by callers.
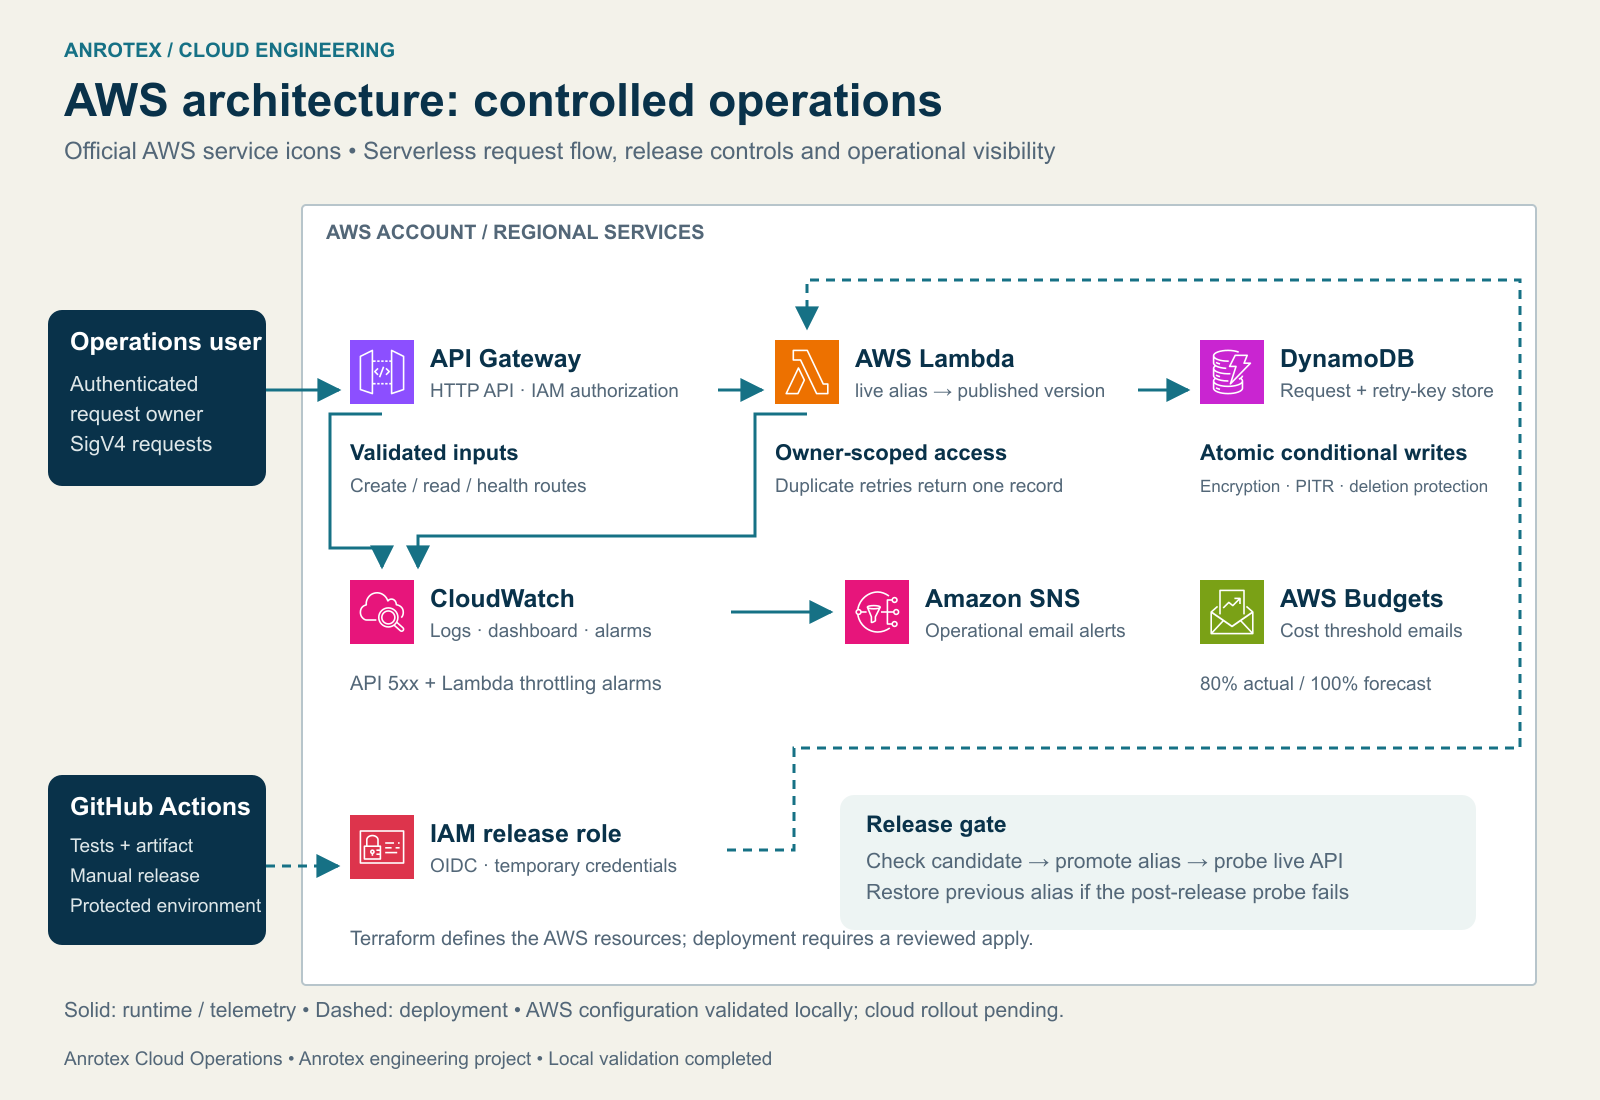
A Python API validates requests, checks ownership and uses atomic DynamoDB writes. Repeating the same request with the same key returns the existing record instead of creating a duplicate.
Terraform defines API Gateway, Lambda, DynamoDB, scoped IAM permissions, logs, alarms and budget notifications. The infrastructure and application releases have separate review steps.
The release script probes a published candidate before moving the live alias. If the subsequent API Gateway checks fail, it requests restoration of the previous version, guarded against concurrent alias changes.
The project includes a local backup and restore exercise, release failure tests and an operating runbook. The workflow uses temporary AWS credentials through GitHub OIDC.
A local exercise sent 100 requests using the same retry key: one record was created and 99 attempts returned it. A separate backup exercise restored 25 records and confirmed that their contents matched.
These checks demonstrate application behavior under the tested conditions. Live service limits, permissions and recovery timing need their own AWS acceptance tests.
Start with an existing AWS workload or one application's release pipeline. We agree the scope, required access and acceptance checks before work starts.
Understand the architecture, cost and reliability priorities for one workload with the US$500 AWS Infrastructure Review.
See review scope and deliverablesBuild, check and deploy one application to an existing AWS staging target with the US$1,500 CI/CD Pipeline Setup.
See pipeline scope and deliverablesNeed broader infrastructure work? Explore our DevOps and Terraform services.